ভূমিকা
রেট-লিমিটিং DOS ও DDOS আক্রমণ থেকে ওয়েবসাইট বাঁচাতে দিনে দিন গুরুত্বপূর্ণ হয়ে উঠছে। এটি ফেক রিকোয়েস্ট বা ব্রুট ফোর্স আক্রমণ থেকে সিস্টেমকে সুরক্ষিত করে। এক্সপ্রেস-রেট-লিমিট একটি NPM প্যাকেজ যা একটি IP-র রিকোয়েস্ট সংখ্যা সীমাবদ্ধ করে।
রেট-লিমিট মডিউল ইনস্টল করা
npm install --save express-rate-limit
উদাহরণ
rateLimit.js ফাইল তৈরি করে নিচের কোড কপি করুন। রান করতে node rateLimit.js কমান্ড দিন।
// Importing the express dependency const express = require("express"); // Importing the express-rate-limit dependency const rateLimit = require("express-rate-limit"); // Storing the express function in variable application const applicaion = express(); // Calling the ratelimiter function with its options // max: Contains the maximum number of requests // windowsMs: Contains the time in milliseconds to receive max requests // message: message to be shown to the user on rate-limit const limiter = rateLimit({ max: 5, windowMs: 60 * 60 * 1000, message: "Too many request from this IP" }); // Adding the rate-limit function to the express middleware so // that each requests passes through this limit before executing applicaion.use(limiter); // GET route for handling the user requests applicaion.get("/", (req, res) => { res.status(200).json({ status: "SUCCESS", message: "Welcome to TutorialsPoint !" }); }); // Server Setup const port = 8000; applicaion.listen(port, () => { console.log(`app is running on port ${port}`); });আউটপুট
C:\home\node>> node rateLimit.js
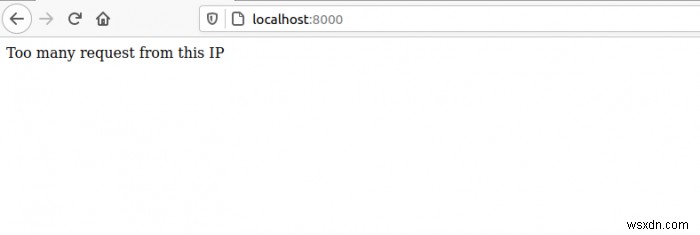
ব্রাউজারে localhost:8000 হিট করুন। ৫ বার سے বেশি রিফ্রেশ করলে নিচের এরর দেখাবে: